Enterprise Cloud Security: Explore Protection Tools, Features and Risk Management
Cloud computing has become an essential part of modern enterprise operations. Businesses use cloud infrastructure to host applications, store sensitive information, manage customer records, operate databases, and support remote teams. Although cloud platforms provide flexibility and scalability, they also introduce security responsibilities that organizations must manage carefully.
Enterprise cloud security focuses on protecting cloud-hosted applications, infrastructure, identities, networks, and information against unauthorized access, data exposure, malicious activity, and operational disruption.
A comprehensive cloud security program combines technical protection tools with policies, monitoring procedures, access controls, and incident response planning. It must also account for the shared responsibility model, under which cloud providers and customers have different security obligations.
This guide explains enterprise cloud security, important protection tools, essential features, common risks, compliance considerations, and practical strategies for improving organizational security.
What Is Enterprise Cloud Security?
Enterprise cloud security refers to the technologies, policies, procedures, and controls used to protect an organization's cloud-based systems and information.
It covers public cloud, private cloud, hybrid cloud, and multicloud environments. Depending on the architecture, security controls may protect virtual machines, containers, databases, cloud applications, storage systems, APIs, and employee identities.
Important areas include:
Identity and access management: Controls who can access cloud resources and what actions they can perform.
Data protection: Uses encryption, classification, access restrictions, and monitoring to protect sensitive information.
Network security: Controls traffic between cloud workloads, users, applications, and external systems.
Threat detection: Identifies suspicious activity, compromised accounts, and potential attacks.
Configuration management: Detects insecure cloud settings and unauthorized infrastructure changes.
Workload protection: Monitors virtual machines, containers, serverless applications, and other cloud workloads.
Compliance management: Helps organizations evaluate security controls against applicable legal, regulatory, and contractual requirements.
Cloud security is not a single product. It is a coordinated approach that combines multiple technologies and operating procedures.
Why Enterprise Cloud Security Matters
A security incident involving cloud infrastructure can affect sensitive information, business applications, customer relationships, and essential operations.
Several factors make enterprise cloud protection important.
Protection of business information: Organizations may store financial records, employee information, customer data, intellectual property, and confidential documents in cloud environments.
Identity-related threats: Compromised credentials and excessive permissions can allow unauthorized individuals to access important systems.
Misconfiguration exposure: Publicly accessible storage, unrestricted network rules, and insecure application settings may expose resources unintentionally.
Business continuity: Cloud attacks, ransomware, and service disruptions can interrupt essential business operations.
Regulatory responsibilities: Organizations may need to demonstrate that appropriate security, privacy, access, and data management controls are in place.
Third-party exposure: Cloud platforms, software vendors, contractors, and integrated applications can introduce additional security dependencies.
Operational visibility: Centralized monitoring helps security teams understand activity across different cloud accounts, regions, and environments.
The objective is to reduce unnecessary exposure, identify threats promptly, and maintain the confidentiality, integrity, and availability of business systems.
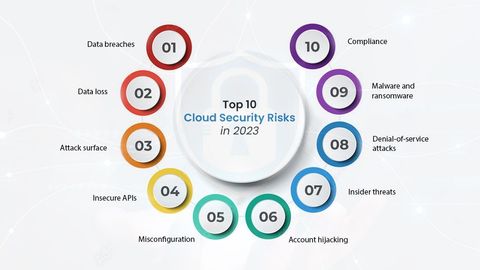
Major Enterprise Cloud Security Risks
Understanding common threats helps organizations select appropriate protection tools and prioritize security investments.
1. Cloud Misconfiguration
Misconfiguration occurs when cloud resources are deployed with insecure or unintended settings.
Examples include:
Publicly accessible storage containing sensitive information.
Unrestricted inbound network access.
Inadequate logging and monitoring.
Excessive permissions assigned to applications.
Unprotected administrative interfaces.
Incorrect encryption settings.
Configuration errors can remain unnoticed when organizations operate multiple cloud accounts or lack consistent security policies.
2. Identity and Access Compromise
Cloud environments depend heavily on digital identities. Employees, administrators, applications, automated workloads, and external partners may all have access to cloud resources.
Common risks include stolen credentials, weak authentication, excessive privileges, poorly managed service accounts, and insecure access tokens.
Organizations should apply least-privilege access, strong authentication, regular permission reviews, and appropriate privileged access controls.
3. Data Exposure and Information Theft
Sensitive information may be exposed through compromised accounts, insecure storage, application vulnerabilities, incorrect permissions, or unauthorized data transfers.
Data protection should cover information at rest, in transit, and during processing where suitable controls are available.
4. API and Application Vulnerabilities
APIs allow applications and cloud services to exchange information. Poor authentication, excessive permissions, weak input validation, and inadequate rate controls can create opportunities for attackers.
Security testing and API monitoring should be incorporated into application development and deployment processes.
5. Insider and Third-Party Risks
Employees, contractors, vendors, and external technology providers may have legitimate access that can be misused or compromised.
Organizations should review third-party permissions, monitor privileged activity, and maintain clear responsibilities for external access.
6. Ransomware and Cloud Workload Attacks
Ransomware and other malicious activity can affect cloud-hosted systems, backups, virtual machines, and connected business applications.
Protection requires layered controls, isolated backups, workload monitoring, recovery testing, and documented incident response procedures.
7. AI-Related Cloud Security Risks
AI applications and automated agents can introduce new security concerns, particularly when they access internal information, APIs, databases, or other cloud resources.
Organizations should monitor AI identities, permissions, data access, model integrations, and the tools that automated agents are authorized to use.
Enterprise Cloud Security Tools and Technologies
Different cloud security tools address different parts of the enterprise environment. Their capabilities may overlap, and some products combine multiple functions.
Cloud Security Posture Management (CSPM)
CSPM tools identify cloud configuration weaknesses and help organizations monitor security settings across cloud environments.
Common capabilities include:
Configuration assessments.
Policy violation detection.
Public exposure identification.
Compliance control mapping.
Security posture reporting.
Remediation prioritization.
CSPM can help security teams identify misconfigured resources before they lead to significant exposure.
Cloud Workload Protection Platforms (CWPP)
CWPP technologies focus on protecting workloads operating in cloud environments.
Depending on the platform, capabilities may include:
Virtual machine monitoring.
Container security.
Runtime threat detection.
Vulnerability assessment.
Workload isolation.
Malware detection.
Application behavior monitoring.
These tools are particularly relevant when an organization operates complex cloud-native applications.
Cloud Access Security Brokers (CASB)
CASB technologies provide visibility and policy enforcement for cloud applications accessed by employees and other users.
Common capabilities include:
Cloud application discovery.
User activity monitoring.
Data loss prevention.
Access policy enforcement.
Risk identification for cloud applications.
Detection of unauthorized application usage.
CASB functionality may be delivered as a standalone product or as part of a broader security platform.
Cloud-Native Application Protection Platforms (CNAPP)
CNAPP combines multiple cloud security capabilities into a more integrated approach.
Depending on the product, it may include:
Cloud security posture management.
Workload protection.
Identity risk assessment.
Vulnerability management.
Infrastructure-as-code scanning.
Cloud entitlement analysis.
Risk prioritization.
The purpose is to provide greater context across cloud configurations, identities, workloads, and application development.
Identity and Access Management (IAM)
IAM technologies manage identities, authentication, authorization, and permissions.
Important capabilities include:
Multifactor authentication.
Single sign-on.
Role-based access control.
Privileged identity management.
Conditional access.
Identity lifecycle management.
Access certification and periodic reviews.
Strong identity controls are central to enterprise cloud security because legitimate credentials are frequently targeted by attackers.
Security Information and Event Management (SIEM)
SIEM platforms collect and analyze security events from cloud services, applications, endpoints, networks, and identity systems.
They can support:
Centralized security monitoring.
Event correlation.
Suspicious activity detection.
Incident investigation.
Audit trail analysis.
Security reporting.
SIEM platforms are often integrated with security orchestration and automated response tools.
Comparison of Enterprise Cloud Security Tools
| Security technology | Primary purpose | Common capabilities |
|---|---|---|
| CSPM | Cloud configuration protection | Misconfiguration detection and posture assessment |
| CWPP | Workload protection | Runtime monitoring and workload security |
| CASB | Cloud application oversight | Application visibility and data protection |
| CNAPP | Integrated cloud protection | Configuration, workload, identity, and vulnerability insights |
| IAM | Identity governance | Authentication and access permissions |
| SIEM | Security monitoring | Event correlation and incident investigation |
| DSPM | Data security posture | Sensitive data discovery and exposure assessment |
| WAF | Application protection | Web traffic inspection and filtering |
A business does not necessarily need every technology as a separate product. Selection should depend on its cloud architecture, existing security tools, data sensitivity, threat exposure, and operational capabilities.
Essential Features to Evaluate in Cloud Security Platforms
Selecting cloud security technology requires more than reviewing a product's feature list. Organizations should determine whether the platform addresses their actual security requirements.
Multicloud visibility: The platform should provide appropriate visibility across the cloud providers and accounts used by the organization.
Identity risk analysis: It should help identify excessive permissions, inactive accounts, suspicious access, and risky service identities.
Configuration monitoring: It should detect insecure settings and provide enough context for corrective action.
Threat detection: It should identify suspicious activity involving accounts, workloads, applications, and data.
Data discovery and classification: It should help identify sensitive information and understand where it is stored and accessed.
Automation: Automated workflows can help prioritize alerts and perform approved response actions.
Integration: The platform should work with existing identity systems, SIEM tools, endpoint security, ticketing platforms, and cloud management systems.
Audit reporting: It should provide useful evidence of security monitoring, access reviews, configuration changes, and control operation.
Scalability: It should support the organization's expected workloads, data volumes, and cloud expansion.
Usability: Security teams should be able to investigate findings and understand remediation priorities without excessive operational complexity.
Cloud Security Architecture and Protection Layers
An effective cloud security architecture uses multiple layers rather than relying on a single defensive control.
Identity and Access Layer
Organizations should establish strong authentication, least-privilege permissions, role-based access, and controlled administrative access.
Human and non-human identities should both be included in access governance.
Network Protection Layer
Network controls can limit unnecessary communication between cloud workloads and external systems.
Relevant measures include network segmentation, firewall policies, private connectivity, secure gateways, and monitoring of unusual traffic.
Application and API Layer
Applications should be developed and configured with secure authentication, authorization, input validation, API protection, and vulnerability management.
Development teams should include security reviews throughout the software lifecycle.
Data Protection Layer
Data protection should include classification, encryption, access restrictions, monitoring, backup arrangements, and appropriate retention procedures.
Sensitive information should only be accessible to authorized identities for legitimate business purposes.
Monitoring and Response Layer
Centralized logging, threat detection, alert correlation, and incident response help organizations investigate suspicious activity.
Logs should be protected against unauthorized modification and retained according to applicable operational and legal requirements.
Enterprise Cloud Security Risk Management Framework
A practical risk management framework helps organizations identify security priorities and maintain consistent controls.
Step 1: Identify Cloud Assets
Create an inventory of cloud accounts, workloads, databases, applications, identities, storage resources, and external integrations.
Identify which systems support critical business operations and which contain sensitive information.
Step 2: Assess Threats and Vulnerabilities
Evaluate misconfigurations, exposed resources, vulnerable software, identity risks, third-party dependencies, and potential data exposure.
Consider both technical weaknesses and organizational factors such as unclear ownership or inadequate access reviews.
Step 3: Prioritize Risks
Not every security finding requires the same level of attention.
Risk prioritization should consider:
Business criticality of the affected resource.
Sensitivity of the information involved.
Internet exposure.
Exploitability of the weakness.
Identity privileges and access paths.
Potential financial or operational impact.
Existing security controls.
A vulnerability in an isolated test environment may require a different response from an exposure involving a critical production database and an overprivileged identity.
Step 4: Implement Appropriate Controls
Select controls that address the identified risks.
Examples include stronger authentication, network restrictions, encryption, configuration guardrails, vulnerability remediation, and data access monitoring.
Step 5: Monitor Security Continuously
Review security alerts, configuration changes, access activity, workload behavior, and data movement.
Monitoring should cover important cloud resources and include procedures for identifying missing logs or failed integrations.
Step 6: Prepare Incident Response Procedures
Establish processes for investigating compromised identities, exposed data, suspicious workloads, and unauthorized configuration changes.
Define escalation responsibilities and ensure that relevant teams understand their roles.
Step 7: Test and Improve
Use controlled security assessments, authorized simulations, access reviews, and recovery exercises to evaluate whether the security program works as intended.
Findings should be tracked until appropriate corrective actions are completed.
Enterprise Cloud Security Compliance and Governance
Cloud security programs often need to support multiple legal, regulatory, industry, and contractual requirements.
In the United States, relevant frameworks and requirements may include:
NIST Cybersecurity Framework 2.0: Provides a structure for governing, identifying, protecting, detecting, responding to, and recovering from cybersecurity risks.
NIST SP 800-53: Provides security and privacy control guidance for information systems and organizations.
FedRAMP: Establishes security assessment and authorization requirements for eligible cloud services used by US federal agencies.
HIPAA: Applies relevant privacy and security obligations to covered entities and business associates handling protected health information.
GLBA: Includes safeguards requirements for covered financial institutions handling customer information.
PCI DSS: Establishes payment card data security requirements for organizations within its applicable scope.
State privacy laws: May impose requirements concerning personal information, data security, and breach notifications.
These frameworks do not automatically apply to every organization. Applicability depends on the business, data, systems, contracts, and jurisdiction.
Organizations should maintain documentation covering security policies, access reviews, risk assessments, vendor oversight, incident records, control testing, and remediation activities.
Recent Enterprise Cloud Security Developments in 2026
Cloud security priorities continue to evolve as organizations expand multicloud operations, adopt AI applications, and manage increasingly complex identities.
October 21, 2026 – SANS Cloud Security Survey: The SANS Institute reported that 93% of surveyed organizations were already running production workloads in the cloud, while only 40% described their cloud security programs as advanced or optimized. The survey identified misconfiguration as the leading cause of critical cloud incidents among respondents, at 45%. These findings highlight the importance of configuration governance, clear ownership, and faster remediation. <Cite refs={["turn641139search1"]}/>
August 2026 – Cloud Security Alliance Top Threats Report: The Cloud Security Alliance identified inadequate identity and access management as its leading cloud security concern. Its report also highlighted AI-enhanced attacks, insecure third-party resources, API weaknesses, misconfiguration, and AI system compromise. <Cite refs={["turn641139search0","turn641139search10"]}/>
2026 – Google Cloud Threat Horizons: Google Cloud's H1 2026 report highlighted identity compromise, data theft, vulnerable third-party software, and permissive firewall configurations as important cloud security concerns. Its analysis of cloud and SaaS-related incident response engagements found identity issues involved in 83% of the examined incidents. This is a finding from the report's particular incident dataset, not a universal industry-wide rate. <Cite refs={["turn641139search4"]}/>
August 21, 2026 – NIST Multicloud Security Draft: NIST published the initial public draft of IR 8613, examining security and compliance challenges in multicloud environments. The report discusses difficulties involving identity management, logging, configuration, data protection, and centralized security controls. The public comment period closed on October 5, 2026; the document should be treated as a draft rather than a finalized standard. <Cite refs={["turn641139search3","turn641139search13"]}/>
These developments reinforce the importance of identity governance, configuration control, integrated monitoring, and consistent protection across cloud environments.
Enterprise Cloud Security Implementation Checklist
Organizations can use this checklist when reviewing their cloud security programs:
Maintain an inventory of cloud accounts, applications, workloads, and data.
Identify critical business systems and sensitive information.
Apply multifactor authentication to important user and administrative accounts.
Review human and non-human identity permissions.
Remove unnecessary access and inactive credentials.
Monitor cloud configurations and exposed resources.
Protect sensitive information through appropriate encryption and access controls.
Secure APIs and application interfaces.
Monitor workloads, containers, and virtual machines.
Centralize important security logs and alerts.
Assess third-party integrations and cloud dependencies.
Establish incident escalation and response procedures.
Test backup restoration and business continuity plans.
Document compliance requirements and control evidence.
Review security findings and remediation progress regularly.
Tools and Resources
The following resources can support enterprise cloud security planning and implementation:
NIST Cybersecurity Framework: Guidance for organizing cybersecurity risk management.
NIST SP 800-53: Security and privacy control reference for enterprise information systems.
CISA: Cloud security guidance, threat advisories, and cybersecurity recommendations.
Cloud Security Alliance: Cloud security research, guidance, and control frameworks.
Microsoft Defender for Cloud: Cloud security posture and workload protection capabilities across supported environments.
AWS Security Hub: Security findings and posture visibility across supported AWS environments.
Google Security Command Center: Security risk visibility and threat detection for Google Cloud environments.
SIEM platforms: Centralized monitoring, event correlation, and security investigation.
Identity governance platforms: Access reviews, permission management, and privileged identity oversight.
Product capabilities and integrations vary by edition and configuration. Organizations should evaluate current vendor documentation and test products against their actual technical and operational requirements.
Frequently Asked Questions
1. What is enterprise cloud security?
Enterprise cloud security is the combination of technologies, policies, and procedures used to protect cloud infrastructure, applications, identities, networks, and data from cyber threats and unauthorized access.
2. Which tools are commonly used for enterprise cloud protection?
Common categories include CSPM, CWPP, CASB, CNAPP, IAM, SIEM, data security posture management, and web application firewalls. Their functions may overlap, and some platforms combine several capabilities.
3. What are the biggest cloud security risks for enterprises?
Common risks include misconfiguration, compromised identities, excessive permissions, data exposure, insecure APIs, vulnerable workloads, third-party compromise, and ransomware.
4. How can organizations improve cloud security?
Organizations can improve protection through strong identity controls, least-privilege access, secure configurations, encryption, vulnerability management, continuous monitoring, incident response preparation, and regular security assessments.
5. Does using a major cloud provider guarantee enterprise security?
No. Cloud providers secure parts of the underlying infrastructure, but customers retain responsibilities for areas such as identities, data, application settings, access permissions, and workload configuration. The precise division of responsibility depends on the provider and cloud deployment model.
Conclusion
Enterprise cloud security requires a coordinated approach to protecting infrastructure, identities, applications, workloads, networks, and sensitive information. Tools such as CSPM, CWPP, CASB, CNAPP, IAM, and SIEM can help organizations identify risks and strengthen protection across cloud environments.
However, technology alone cannot guarantee security. Effective programs also require clear ownership, disciplined access management, reliable configuration controls, continuous monitoring, incident response planning, and regular review.
Businesses should begin by identifying their most important cloud assets, assessing exposure, and prioritizing controls according to business risk. A structured approach can improve visibility, reduce avoidable weaknesses, and support more resilient enterprise cloud operations.

Related Post...
Enterprise CRM Software: Discover Business Features, Automation and Analytics
Updated: November 03, 2026
Read More